
By Jackson Godwin. Cybersecurity Analyst & Penetration Tester.
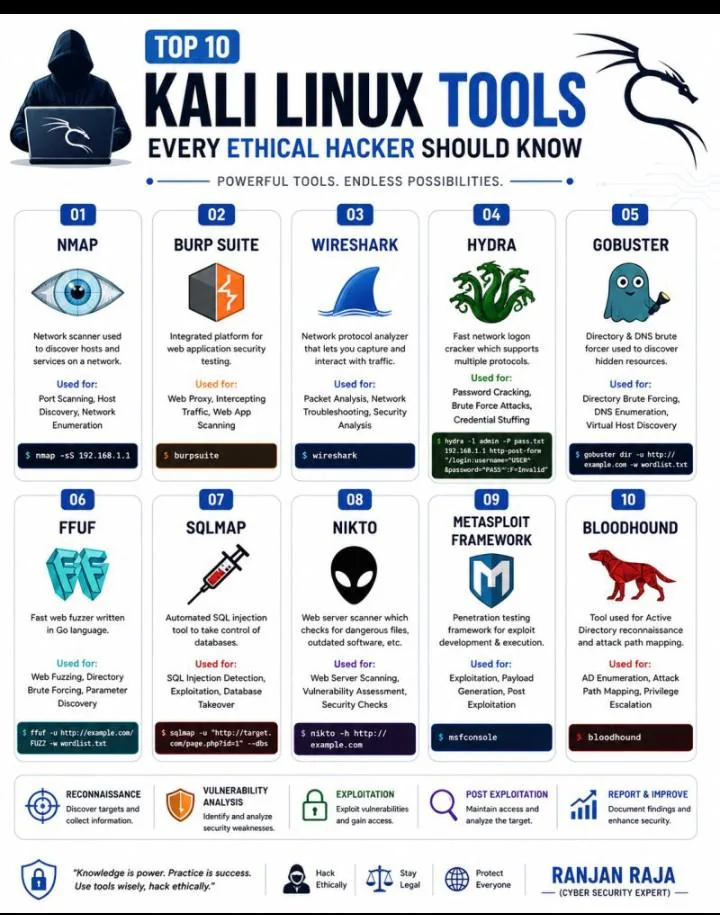
Kali Linux remains the most popular operating system for ethical hackers, penetration testers, and cybersecurity professionals worldwide.
Developed specifically for security testing, Kali Linux comes with hundreds of tools designed to help security professionals identify vulnerabilities before cybercriminals can exploit them.
Whether you’re preparing for a career in cybersecurity or seeking to enhance your penetration testing skills, mastering the right tools is crucial.
In this guide, we’ll explore the Top 10 Kali Linux Tools Every Ethical Hacker Uses in 2026 and explain how each one contributes to modern cybersecurity assessments.
1. Nmap (Network Mapper)
Nmap is one of the first tools every ethical hacker learns.
It helps security professionals discover hosts, identify open ports, detect operating systems, and map network services.
What Nmap Can Do
- Host discovery
- Port scanning
- Service detection
- OS fingerprinting
- Vulnerability identification
Example Command
nmap -sV 192.168.1.1This command identifies running services and software versions on the target system.
Why Ethical Hackers Love It
Before testing a target, you need to know what’s running. Nmap provides that visibility quickly and efficiently.
2. Burp Suite
Burp Suite is one of the most widely used web application security testing tools.
It acts as an intercepting proxy between your browser and the target application.
Key Features
- Intercept HTTP requests
- Modify web traffic
- Identify vulnerabilities
- Test authentication mechanisms
- Analyze web application security
Common Use Cases
- SQL Injection testing
- Cross-Site Scripting (XSS) testing
- Session management analysis
- API security testing
3. Metasploit Framework
Metasploit is one of the most powerful penetration testing frameworks available.
It allows security professionals to validate vulnerabilities in controlled environments.
Key Features
- Exploit development
- Payload generation
- Vulnerability validation
- Post-exploitation assessment
Why It’s Popular
Metasploit helps organizations understand the real-world impact of vulnerabilities that scanners identify.
4. Wireshark
Wireshark is the world’s most popular network protocol analyzer.
It allows security professionals to capture and inspect network traffic in real time.
What Wireshark Can Analyze
- HTTP traffic
- DNS requests
- TCP communications
- SSL/TLS traffic
- Network troubleshooting
Example Display Filter
httpThis filter displays HTTP traffic captured on the network.
Why Ethical Hackers Use It
Understanding network traffic is fundamental to identifying suspicious activity and security weaknesses.
5. SQLmap
SQLmap automates the detection and testing of SQL injection vulnerabilities.
Key Features
- SQL injection detection
- Database fingerprinting
- Database enumeration
- Security assessment
Example Command
sqlmap -u "http://example.com/page?id=1"Why It’s Valuable
SQL injection remains one of the most dangerous web application vulnerabilities.
6. WPScan
WPScan focuses specifically on WordPress security assessments.
Since WordPress powers a significant portion of the internet, it remains a valuable tool for security professionals.
WPScan Can Identify
- Vulnerable plugins
- Weak passwords
- Outdated WordPress versions
- Security misconfigurations
Example Command
wpscan --url https://example.com7. Hydra
Hydra is a password auditing and authentication testing tool.
It supports numerous protocols and helps security professionals evaluate authentication security.
Supported Services
- SSH
- FTP
- HTTP
- RDP
- SMTP
Why It’s Useful
Organizations can use Hydra during authorized security assessments to evaluate password policy effectiveness.
8. John the Ripper
John the Ripper is a password auditing tool used to assess password strength.
Key Features
- Password hash analysis
- Password auditing
- Dictionary attacks
- Security testing
Why Ethical Hackers Use It
Weak passwords remain one of the most common security issues in organizations.
9. Aircrack-ng
Aircrack-ng is a wireless security testing suite.
Features
- Wireless network assessment
- Packet capture
- Wireless analysis
- Security auditing
Common Uses
- Wireless security testing
- Network auditing
- Security training
Why It’s Important
Wireless networks continue to be attractive targets for attackers, making wireless security skills highly valuable.
10. Nikto
Nikto is an open-source web server scanner.
It helps identify common web server vulnerabilities and misconfigurations.
What Nikto Detects
- Outdated software
- Default files
- Dangerous configurations
- Known vulnerabilities
Example Command
nikto -h example.comWhy Security Professionals Use It
Nikto provides a quick overview of web server security issues.
How These Tools Fit into a Penetration Test
A typical penetration test might use:
| Phase | Tool |
|---|---|
| Reconnaissance | Nmap |
| Vulnerability Identification | Nikto, WPScan |
| Web Application Testing | Burp Suite |
| Network Analysis | Wireshark |
| Password Auditing | Hydra, John the Ripper |
| Wireless Assessment | Aircrack-ng |
| Validation & Assessment | Metasploit |
| Database Security Testing | SQLmap |
Together, these tools provide visibility into different aspects of an organization’s security posture.
Which Tool Should Beginners Learn First?
If you’re new to cybersecurity, start with:
Beginner Roadmap
- Nmap
- Wireshark
- Burp Suite
- Nikto
- SQLmap
- Metasploit
- WPScan
- Hydra
- John the Ripper
- Aircrack-ng
This learning path builds a strong foundation in networking, web security, and vulnerability assessment.
Frequently Asked Questions (FAQ)
Is Kali Linux legal?
Yes. Kali Linux is a legitimate operating system used by security professionals, researchers, and students. However, you should only test systems you are authorized to assess.
Which Kali Linux tool is most important?
Nmap is often considered the most fundamental tool because it helps identify systems, services, and network exposure.
Do professional penetration testers use these tools?
Yes. Many professional security consultants use these and similar tools during authorized assessments, alongside commercial platforms and custom scripts.
Is Kali Linux suitable for beginners?
Yes, although a basic understanding of Linux, networking, and cybersecurity concepts is helpful.
Final Thoughts
Kali Linux remains one of the most powerful platforms for ethical hacking and penetration testing.
While the operating system contains hundreds of tools, mastering these ten will provide a strong foundation for network security, web application testing, password auditing, wireless security, and vulnerability assessment.
Remember that tools alone do not make an ethical hacker. Understanding networking, operating systems, security principles, and responsible testing practices is just as important.
Start with Nmap and Wireshark, build your skills gradually, and continue learning through hands-on labs and authorized practice environments.
About the Author
Jackson Godwin is a Cybersecurity Consultant specializing in Vulnerability Assessment and Penetration Testing (VAPT), Governance, Risk and Compliance (GRC), Cloud Security, Enterprise Security, and Banking Cybersecurity. Through JacksonTechnology.com.ng, he shares practical cybersecurity tutorials, penetration testing guides, compliance resources, and career advice to help aspiring security professionals develop real-world cybersecurity skills.