
By Jackson Godwin. Cybersecurity Analyst & Penetration Tester.
Disclaimer
This tool is intended for authorized security assessments and bug bounty use only. Unauthorized reconnaissance is illegal. Users are fully responsible for their actions and must comply with all applicable laws and program policies.
Hey everyone! We’re back with another great tool to add to your bug-hunting arsenal. As always, we’re focused on helping you get the best results from your security research – and today’s tool does exactly that by making subdomain discovery faster and easier than ever!
Dependencies Must be Installed
The tool is securely configured within the Python language, so we need to install Python and some related dependencies first before we can operate the tool.
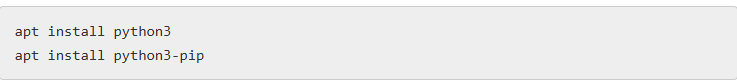
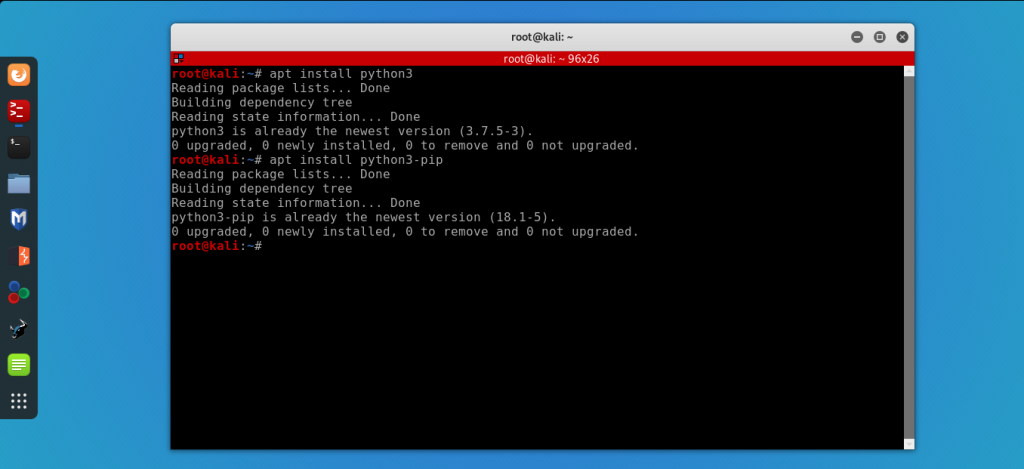
Sublist3r Tool Installation
Now, coming to the second part of this tool, where we will first download the project from Github, go to the directory and download the required dependencies.
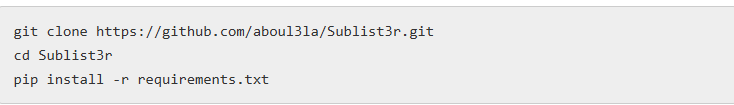
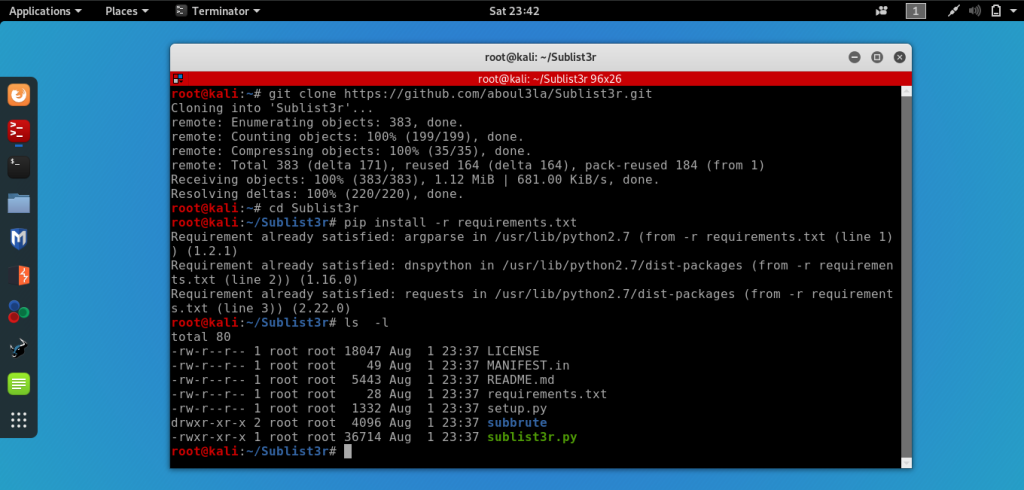
Done :0 !! Everything is set up perfectly, and now we can operate this tool directly through Python commands.

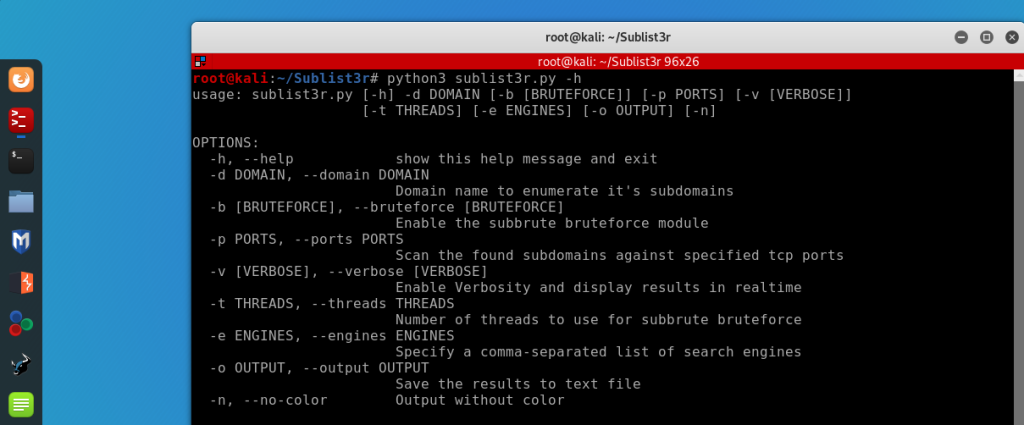
Find Subdomain
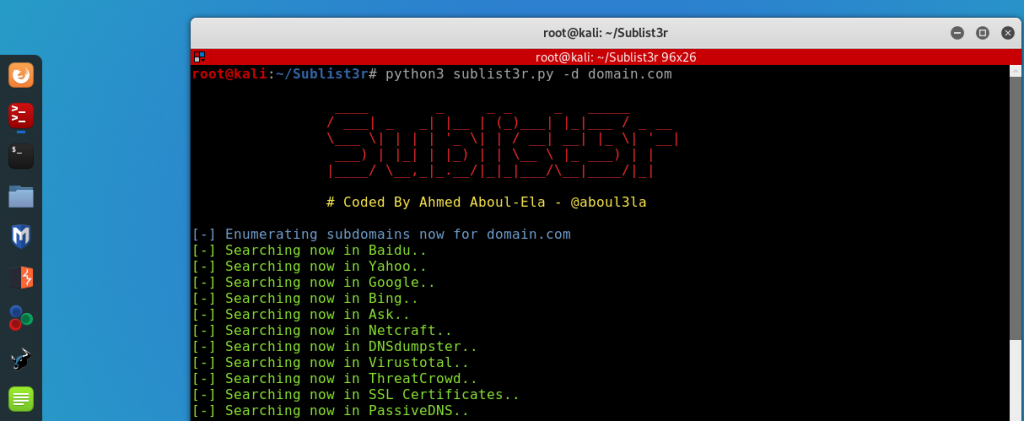
Finding subdomains through this tool is quite simple, as all we have to do is enter the domain name, and that’s it.

Defensive Recommendations:
1. Enforce Uniform Security Policies
Apply the same security controls to all subdomains that you apply to your primary production domain. This includes:
- Strong authentication (MFA, SSO)
- Regular patching and vulnerability scanning
- Web application firewalls (WAF)
- Secure headers (HSTS, CSP, X-Frame-Options)
2. Restrict Public Access to Dev/Test Subdomains
Where possible, restrict access to development and staging subdomains using:
- IP whitelisting
- VPN or zero-trust network access
- Basic authentication with strong credentials
- Internal DNS resolution (not publicly resolvable)
3. Conduct Regular Security Audits
Include all subdomains in your regular security assessments:
- Vulnerability scans
- Penetration testing
- Configuration reviews
- Patch management cycles
4. Monitor Subdomains Continuously
Implement monitoring for:
- Unauthorized changes to subdomain content
- Anomalous traffic patterns
- Outdated software versions
- Newly discovered vulnerabilities affecting subdomains
5. Implement a Subdomain Takeover Prevention Program
- Maintain an up-to-date inventory of all subdomains and their purposes.
- Remove stale or unused subdomains and DNS records.
- Monitor for dangling CNAMEs pointing to decommissioned services.
6. Educate Development and Operations, Teams
Ensure all teams understand that subdomains are part of the attack surface and require the same level of security as production. Provide clear guidelines for:
- Secure deployment pipelines
- Environment isolation
- Credential management
Summary Checklist:
| Action | Status |
|---|---|
| Apply same security controls to all subdomains | [ ] |
| Restrict access to dev/test subdomains (IP whitelist, VPN) | [ ] |
| Include all subdomains in vulnerability scans | [ ] |
| Monitor subdomains for unauthorized changes | [ ] |
| Remove stale DNS records | [ ] |
| Educate dev/ops teams on subdomain security |
About the Author
Jackson Godwin is a Cybersecurity Consultant specializing in Vulnerability Assessment and Penetration Testing (VAPT), Governance, Risk and Compliance (GRC), Information Security, and Enterprise Security Assessments. He has experience assessing web applications, banking systems, and enterprise environments to identify security vulnerabilities and improve organizational resilience.
Through JacksonTechnology.com.ng, Jackson shares practical cybersecurity tutorials, penetration testing guides, compliance resources, and career advice to help professionals and businesses strengthen their cybersecurity posture.