Can a Business Administration Graduate Become a Cybersecurity Professional? My Journey
July 10, 2026
Com 0
By Jackson Godwin. Cybersecurity Analyst & Penetration Tester
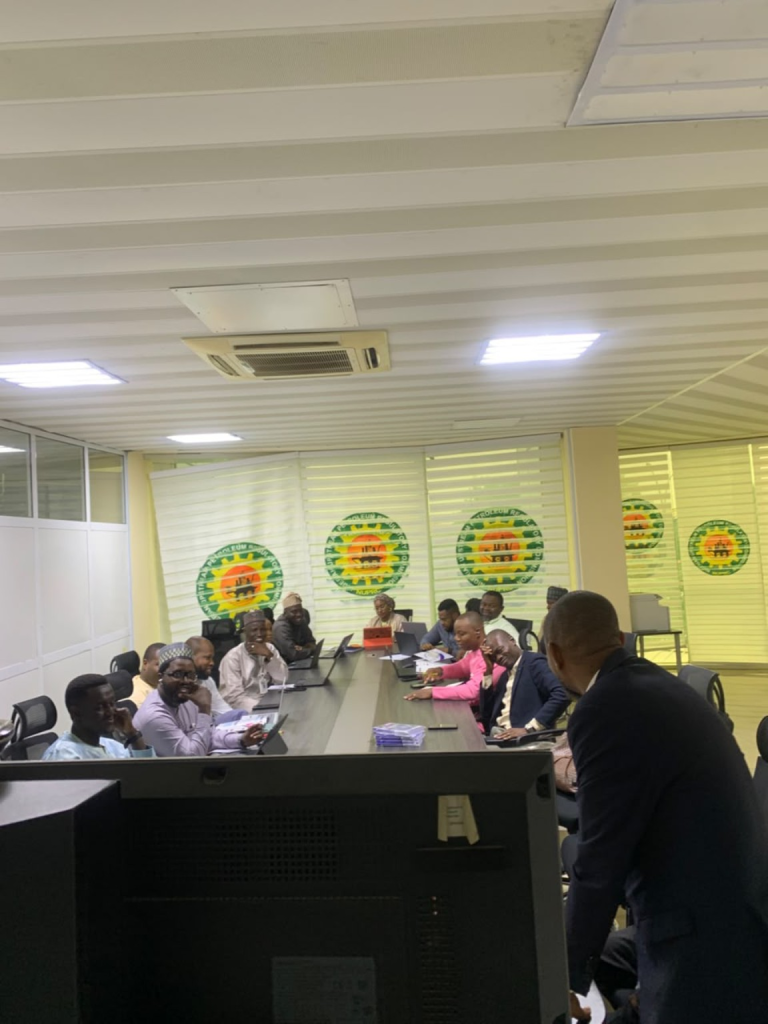
My transition into cybersecurity has been built through continuous learning, teamwork, and real-world project experience. Every meeting, assessment, and engagement has contributed to my professional growth.
Introduction
When I graduated with a Bachelor’s degree in Business Administration from Nasarawa State University, Keffi (NSUK), I never imagined that I would one day build a career in cybersecurity.
Like many graduates, I initially believed my career would be in banking, business management, or administration. Technology was interesting to me, but I had no background in Computer Science or Software Engineering.
Today, I work as a Cybersecurity Consultant, helping organizations identify vulnerabilities, improve their security posture, conduct penetration testing, and implement governance and compliance frameworks.
My journey wasn’t easy, but it taught me that your university degree does not determine your future—your willingness to learn does.
My Career Didn’t Start in Cybersecurity
After graduating, I explored different opportunities while trying to discover where my passion truly belonged.
During that period, I realized something important:
Technology was shaping every industry.
Banks, hospitals, governments, and businesses all depended on secure information systems.
That realization sparked my curiosity.
I started researching ethical hacking, penetration testing, vulnerability assessments, and information security.
The more I learned, the more I became convinced that cybersecurity was the career I wanted to pursue.
Learning from the Ground Up
Starting without a technical degree meant I had to build my knowledge step by step.
I focused on understanding the fundamentals before moving into advanced topics.
Some of the first areas I studied included:
Computer networking
Linux operating systems
Windows administration
Web application security
Cyber threats
Risk management
Information Security principles
At times, the concepts felt difficult, but I reminded myself that every cybersecurity professional was once a beginner.
Building Practical Skills
Reading books alone wasn’t enough.
I wanted practical experience.
I installed Kali Linux and built a home lab where I could safely practice penetration testing techniques.
I learned to use tools such as:
Kali Linux
Burp Suite
Wireshark
Nmap
Metasploit
OWASP ZAP
VirtualBox
Every vulnerability I discovered in my lab improved my confidence.
The more I practiced, the more I understood how attackers think—and how organizations can defend themselves.
My First Professional Opportunity
Eventually, I had the opportunity to participate in real cybersecurity projects.
Working with experienced professionals exposed me to real-world challenges that no textbook could fully explain.
I gained hands-on experience in:
Vulnerability Assessment and Penetration Testing (VAPT)
Security Risk Assessments
ISO/IEC 27001 implementation
Governance, Risk, and Compliance (GRC)
Banking cybersecurity
Technical report writing
Security awareness
These projects helped transform my theoretical knowledge into practical expertise.
How Business Administration Became My Advantage
Many people assume Business Administration and Cybersecurity have nothing in common.
My experience has shown the opposite.
My business background helped me develop skills in:
Communication
Leadership
Business processes
Risk management
Problem-solving
Report writing
Stakeholder engagement
Today, these skills help me explain technical security risks to executives, managers, and clients in a way they can understand.
Cybersecurity isn’t just about technology—it is about protecting business operations.
Challenges Along the Way
The journey wasn’t without obstacles.
Some of the biggest challenges I faced included:
Learning technical concepts from scratch
Overcoming self-doubt
Finding affordable learning resources
Balancing work with continuous study
Keeping up with rapidly changing cyber threats
Each challenge made me more determined to succeed.
Lessons I Learned
If I could give advice to anyone changing careers, it would be this:
Never Stop Learning
Cybersecurity changes every day.
Continuous learning is essential.
Practice More Than You Read
Build a lab.
Break things.
Fix them.
Experience is your greatest teacher.
Your Degree Is Not Your Limitation
Many successful cybersecurity professionals come from non-technical backgrounds.
Curiosity and persistence matter more than the title on your certificate.
Soft Skills Matter
Communication, teamwork, leadership, and business knowledge are just as valuable as technical skills.
My Advice to Career Changers
If you’re considering a move into cybersecurity, start with the basics.
Learn networking.
Understand Linux.
Practice using free tools.
Build a home lab.
Create projects.
Earn certifications when you can.
Most importantly, stay consistent.
Progress may feel slow at first, but every skill you gain moves you closer to your goal.
Looking Ahead
Cybersecurity continues to evolve, and so does my journey.
Every project presents new challenges and new opportunities to learn.
My goal is to continue helping organizations strengthen their security while mentoring others who want to build successful careers in cybersecurity.
Final Thoughts
Transitioning from Business Administration to cybersecurity has been one of the most rewarding decisions of my life.
The path wasn’t always straightforward, but every challenge helped shape the professional I am today.
If you’re thinking about changing careers, don’t let fear or your academic background stop you.
With determination, continuous learning, and practical experience, you can build a successful career in cybersecurity too.
About the Author
Jackson Godwin is a Cybersecurity Consultant specializing in Vulnerability Assessment and Penetration Testing (VAPT), Governance, Risk and Compliance (GRC), Information Security, and Banking Cybersecurity. He shares practical cybersecurity insights, tutorials, and career guidance through JacksonTechnology.com.ng to help professionals and businesses improve their cybersecurity posture.