By Jackson Godwin. Cybersecurity Analyst & Penetration Tester.
Disclaimer Hey folks – pwnSpoof is made for learning and ethical testing only! It’s great for practicing log analysis, testing your SIEM, or running red-team simulations. Please don’t use it for anything illegal or shady – always get proper permission first. Stay ethical, stay safe!
In today’s tutorial, we introduce pwnSpoof – a powerful tool developed by Punk Security that generates realistic spoofed log files for popular web servers. With fully customizable attack scenarios, each log bundle is uniquely crafted, making it an ideal resource for creating Capture The Flag (CTF) scenarios and conducting security training exercises.
Installation
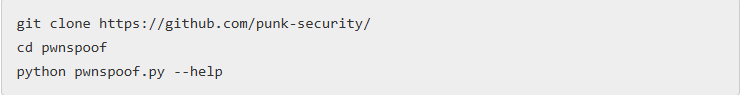
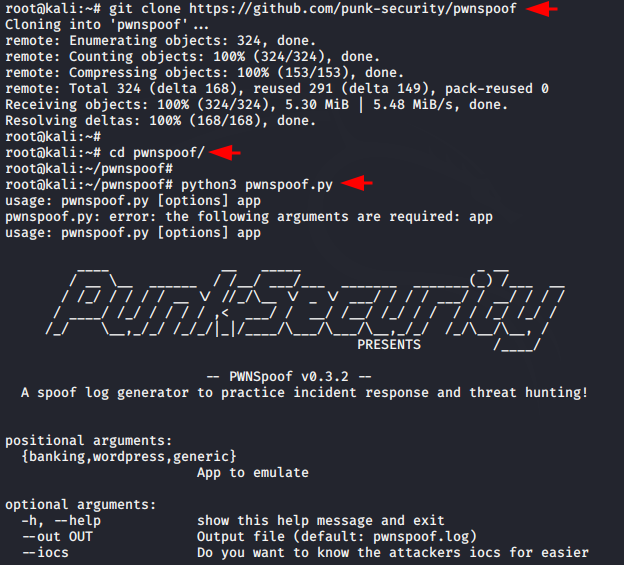
It is quite easy to deploy this tool in any Kali Linux operating system. First, we need to clone the repository from GitHub via the git clone command, enter the directory, and that’s it. Now we can operate this tool with the help of “python3 Utility
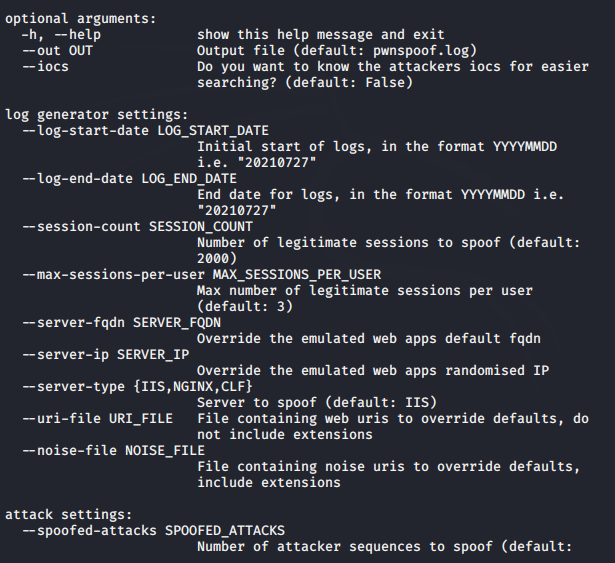
Hmm 🙂 !! Like other tools, it also has a help command, which we can use to find the use case of this tool
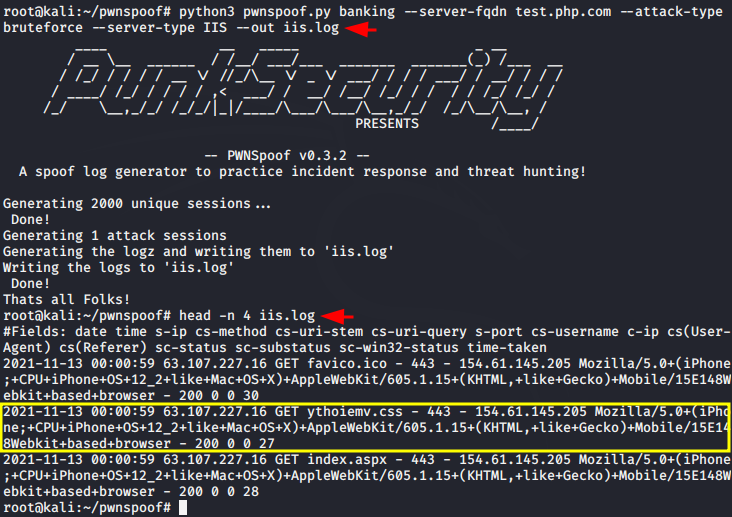
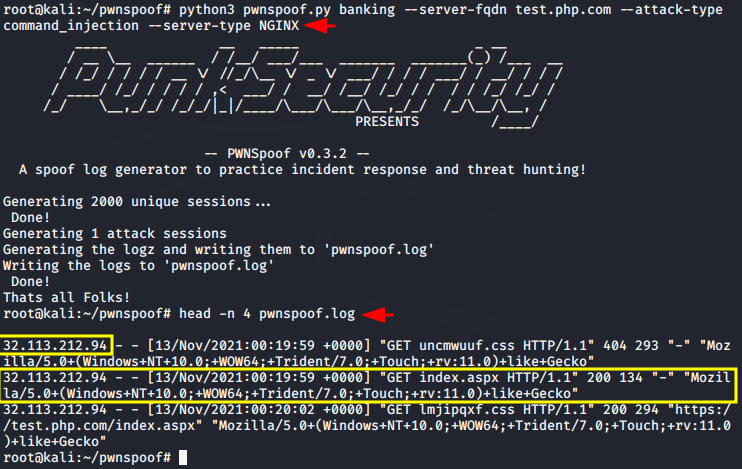
We’re excited to see how impressive the results we get with this tool. First, we attempt to generate fake IIS logs for a website and achieve success. As you can see below, it has generated all the logs in order, which looks very real.
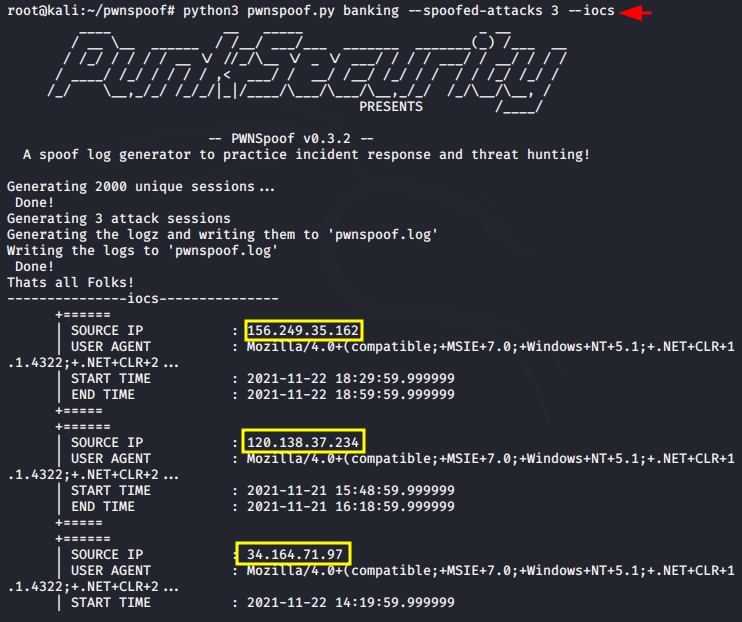
Attackers IP Address
This feature will allow us to create spoof logs with different IP addresses so that the logs look impressive
About the Author
Jackson Godwin is a Cybersecurity Consultant specializing in Vulnerability Assessment and Penetration Testing (VAPT), Governance, Risk and Compliance (GRC), ISO 27001, PCI DSS, Cloud Security, and Enterprise Security. Through JacksonTechnology.com.ng, he shares practical compliance guides, cybersecurity tutorials, penetration testing resources, and security best practices to help organizations strengthen their cyber resilience.
Disclaimer pwnSpoof is a simulation tool intended for authorized security training and testing environments only. Unauthorized use to create deceptive or false log entries is illegal. Users are fully responsible for their actions and must ensure compliance with all applicable laws.