By Jackson Godwin. Cybersecurity Analyst & Penetration Tester.
Practical Cybersecurity Training, Compliance Education and Security Assessment Services
Cybersecurity is no longer only a concern for large technology companies. Businesses of all sizes now depend on websites, cloud platforms, applications, payment systems and digital infrastructure to operate.
As organizations become more dependent on technology, they also face increasing cybersecurity risks, including data breaches, ransomware, phishing, vulnerable applications, unauthorized access, payment-card risks and regulatory compliance challenges.
At JacksonTechnology, we provide cybersecurity-focused training, security assessment and compliance support designed to help individuals, IT professionals, businesses and organizations improve their cybersecurity knowledge and security posture.
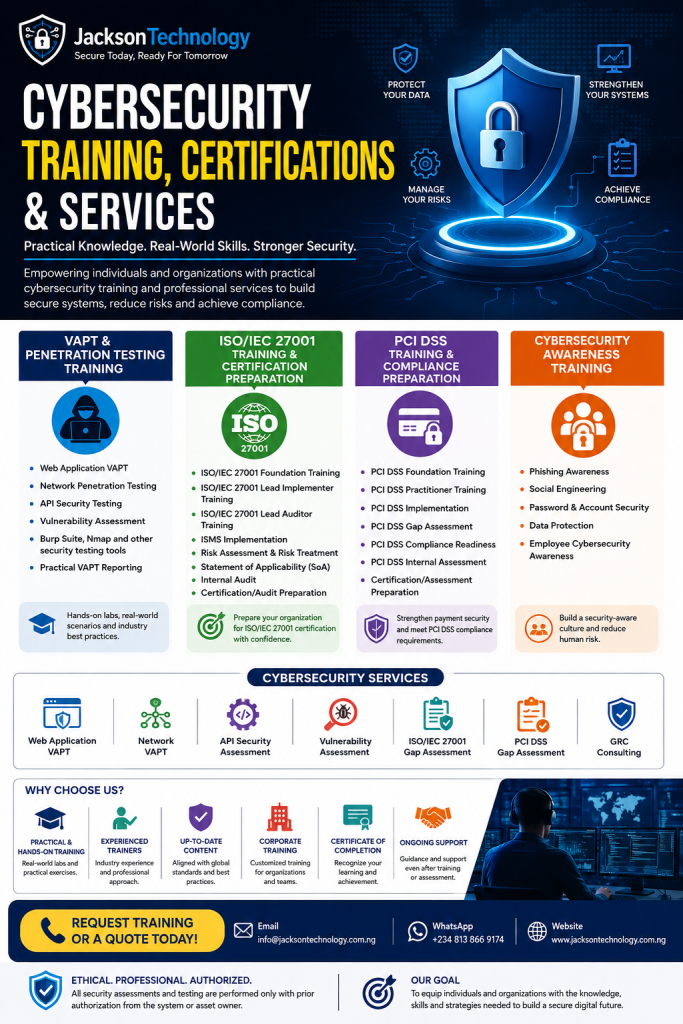
Our areas of focus include Vulnerability Assessment and Penetration Testing (VAPT), penetration-testing training, ISO/IEC 27001 training and implementation support, PCI DSS training and compliance preparation, cybersecurity awareness training, and GRC services.
VAPT & Penetration Testing Training
Vulnerability Assessment and Penetration Testing (VAPT) is an important part of modern cybersecurity.
Vulnerability assessment helps organizations identify weaknesses in systems and applications, while penetration testing involves authorized security testing to determine whether identified weaknesses can be exploited and what impact they could have.
Our VAPT training is designed for people who want to develop practical cybersecurity and penetration-testing skills.
VAPT Training Topics
Training can cover areas such as:
- Web application security testing
- Network penetration testing
- API security testing
- Vulnerability assessment
- Reconnaissance and information gathering
- Port and service enumeration
- Vulnerability identification and validation
- Authentication and authorization testing
- OWASP-based web application testing
- Security testing methodologies
- Vulnerability prioritization
- CVSS risk scoring
- Penetration-testing documentation
- Technical security reporting
- Remediation recommendations
- Practical security testing workflows
Security Testing Tools
Depending on the training requirements, practical sessions may introduce participants to security tools such as:
- Burp Suite
- Nmap
- Nikto
- Nuclei
- OWASP ZAP
- Wireshark
- Metasploit
- WPScan
- SQLmap
- Nessus and other vulnerability-scanning technologies
Training activities should always be performed against systems that participants own or have explicit authorization to test.
Who Is VAPT Training For?
VAPT training can be useful for:
- Cybersecurity beginners
- Penetration testers
- Security analysts
- SOC analysts
- IT professionals
- Network administrators
- Web developers
- System administrators
- Students interested in ethical hacking
- Organizations building internal security teams
The objective is not simply to teach participants how to use security tools, but to help them understand why security weaknesses occur, how they can be validated safely, how risks should be communicated, and how organizations can remediate them.
ISO/IEC 27001 Training & Certification Preparation
ISO/IEC 27001 is an internationally recognized standard for establishing, implementing, maintaining and continually improving an Information Security Management System (ISMS).
Organizations use an ISMS to establish a structured approach to managing information-security risks.
Our ISO/IEC 27001 training and consulting-focused education can help professionals and organizations understand the principles behind information-security management and prepare for implementation or certification activities.
ISO/IEC 27001 Training Areas
Depending on the selected training program, topics may include:
- ISO/IEC 27001 fundamentals
- Information Security Management Systems (ISMS)
- Organizational context
- Leadership and information-security responsibilities
- Risk assessment
- Risk treatment
- Information-security objectives
- Security policies
- Statement of Applicability (SoA)
- Information-security controls
- Internal audits
- Corrective actions
- Continual improvement
- Documentation and evidence
- Certification preparation
ISO/IEC 27001 Training Options
Training can be structured around different professional objectives, including:
ISO/IEC 27001 Foundation Training
Designed to introduce participants to ISO/IEC 27001, ISMS concepts, information-security risk management and the certification process.
ISO/IEC 27001 Lead Implementer Training
Focused on professionals involved in establishing, implementing and maintaining an ISMS.
ISO/IEC 27001 Lead Auditor Training
Focused on professionals who want to understand the principles and practices involved in auditing an ISMS.
ISO/IEC 27001 Gap Assessment
Organizations that are preparing for ISO/IEC 27001 certification can also benefit from a gap assessment.
A gap assessment can help identify:
- Existing controls
- Missing controls
- Documentation gaps
- Risk-management weaknesses
- Evidence gaps
- Policy deficiencies
- Areas requiring corrective action
The result can be used to develop a practical remediation roadmap before an organization proceeds to a formal certification audit.
Important Certification Notice
Training and certification preparation are different from issuing an official ISO/IEC 27001 certificate.
Where formal certification is required, organizations should undergo the appropriate certification process with a qualified and recognized certification body.
Our role may include training, implementation guidance, gap assessment, audit preparation and cybersecurity consulting, depending on the engagement.
PCI DSS Training & Compliance Preparation
Organizations that store, process or transmit payment-card data need to understand their security responsibilities under the applicable Payment Card Industry Data Security Standard (PCI DSS) requirements.
PCI DSS focuses on protecting payment-card data and establishing appropriate security controls around cardholder-data environments.
Our PCI DSS-focused training can help cybersecurity professionals, IT teams, compliance teams and businesses understand important PCI DSS concepts and prepare for compliance activities.
PCI DSS Training Topics
Training may cover:
- PCI DSS fundamentals
- Cardholder data
- Cardholder Data Environment (CDE)
- Security controls
- Access control
- Authentication
- Vulnerability management
- Secure configuration
- Network security
- Logging and monitoring
- Malware protection
- Encryption
- Secure software development
- Security testing
- Incident response
- Third-party service providers
- Compliance documentation
- Evidence collection
- Gap assessment
- Remediation planning
PCI DSS Gap Assessment
A PCI DSS gap assessment can help an organization understand where its current security controls differ from applicable PCI DSS requirements.
A typical assessment may examine areas such as:
- Policies and procedures
- Network architecture
- Access controls
- User authentication
- Vulnerability management
- Security testing
- Logging and monitoring
- Encryption
- Incident response
- Secure software development
- Third-party relationships
The outcome can be used to create a prioritized remediation plan.
PCI DSS Compliance Preparation
Organizations preparing for a PCI DSS assessment may need assistance understanding:
- What evidence should be collected
- Which controls need improvement
- How security processes should be documented
- How vulnerabilities should be addressed
- How security testing should be organized
- How compliance gaps should be prioritized
Training and consulting can help organizations prepare, but formal PCI DSS validation or attestation requirements depend on the organization’s circumstances and the applicable assessment process.
Cybersecurity Awareness Training
Technology alone cannot protect an organization from every cyber threat.
Employees and users are an important part of an organization’s overall security posture.
Cybersecurity awareness training can help employees recognize common threats and understand their responsibilities when handling company information and systems.
Cybersecurity Awareness Topics
Training can cover:
- Phishing
- Business email compromise
- Social engineering
- Password security
- Multifactor authentication
- Safe browsing
- Malware awareness
- Suspicious attachments
- Fraudulent websites
- Mobile-device security
- Data protection
- Remote-work security
- Social-media security
- Physical security
- Incident reporting
Why Cybersecurity Awareness Matters
An employee who recognizes a phishing attempt before clicking a malicious link can prevent a potential security incident.
Awareness training therefore complements technical controls such as firewalls, endpoint protection, email security, identity management and monitoring.
Cybersecurity Services
In addition to training, cybersecurity assessment and consulting services can help organizations identify security weaknesses and improve their security controls.
Web Application VAPT
Web applications can contain vulnerabilities involving authentication, authorization, input validation, session management, business logic and configuration.
Authorized web application security testing can help organizations identify and address these weaknesses before attackers exploit them.
Network VAPT
Network security assessments can help organizations identify vulnerabilities in externally exposed and internally accessible systems.
Testing may include:
- Network discovery
- Port and service enumeration
- Vulnerability identification
- Configuration review
- Authentication testing
- Security-control validation
- Risk assessment
- Remediation recommendations
API Security Assessment
Modern applications increasingly depend on APIs.
API security assessments can examine areas such as:
- Authentication
- Authorization
- Access control
- Input validation
- Rate limiting
- Sensitive data exposure
- API configuration
- Business logic
- Session management
Vulnerability Assessment
A vulnerability assessment helps organizations identify known weaknesses across applications, systems, networks and infrastructure.
The assessment can include vulnerability identification, risk classification, prioritization and remediation recommendations.
ISO/IEC 27001 Gap Assessment
Organizations preparing for ISO/IEC 27001 can use a gap assessment to understand their current level of readiness.
The assessment can identify gaps across areas such as:
- ISMS requirements
- Risk management
- Policies
- Procedures
- Controls
- Documentation
- Evidence
- Internal audit readiness
PCI DSS Gap Assessment
PCI DSS gap assessments can help organizations understand their current security posture against applicable PCI DSS requirements and identify areas requiring remediation.
GRC Consulting
Governance, Risk and Compliance (GRC) is an important component of modern cybersecurity.
GRC-focused support can include areas such as:
- Cybersecurity risk assessment
- Risk registers
- Control assessments
- Security policies
- Compliance gap assessments
- Audit preparation
- Security governance
- Third-party risk
- ISO/IEC 27001 support
- PCI DSS compliance preparation
Who Can Benefit From Our Training and Services?
Our cybersecurity training and consulting services can be useful for:
Individuals
- Students
- Cybersecurity beginners
- IT professionals
- Security analysts
- Penetration testers
- Network professionals
- Compliance professionals
- Auditors
Businesses
- Fintech companies
- Technology companies
- Software companies
- E-commerce businesses
- Professional-service organizations
- Startups
- SMEs
- Organizations handling sensitive information
IT & Security Teams
Organizations can arrange training for internal teams that need to improve their practical cybersecurity, compliance or security-awareness capabilities.
Corporate Cybersecurity Training
Organizations can also request customized cybersecurity training for their employees or technical teams.
Corporate training can be adapted to the organization’s:
- Industry
- Technology environment
- Security objectives
- Employee skill level
- Compliance requirements
- Risk profile
Training can be delivered around practical scenarios relevant to the organization.
For example, a financial-services organization may require training focused on phishing, payment security, PCI DSS, application security and incident response.
A software company may require training focused on secure development, API security, web application testing and vulnerability management.
Why Practical Training Matters
Cybersecurity is not only about memorizing definitions.
Professionals need to understand how security principles apply to real environments.
That is why practical cybersecurity training should combine:
Knowledge + Demonstration + Practical Exercises + Analysis + Reporting
For VAPT training, participants should understand not only how to run a scanner but also how to interpret results, validate vulnerabilities, determine risk and communicate findings.
For ISO/IEC 27001 training, participants should understand not only the standard but also how risk management, controls, documentation and continual improvement work together.
For PCI DSS training, participants should understand how security controls translate into practical protection of payment-card data.
Request Cybersecurity Training or Services
Are you looking for:
- VAPT training?
- Penetration-testing training?
- ISO/IEC 27001 training?
- ISO/IEC 27001 implementation support?
- ISO/IEC 27001 certification preparation?
- PCI DSS training?
- PCI DSS compliance preparation?
- PCI DSS gap assessment?
- Cybersecurity awareness training?
- Web application VAPT?
- Network security assessment?
- API security assessment?
- GRC consulting?
We would be happy to discuss your requirements and determine the appropriate training or cybersecurity service.
Request Training or a Security Assessment
Contact us with:
- Your name
- Organization
- Email address
- Phone/WhatsApp number
- Training or service required
- Number of participants, if applicable
- Preferred training date
- Brief description of your requirements
Important: All penetration-testing and security-assessment activities must be performed with appropriate authorization from the system or asset owner.
Frequently Asked Questions
Do you provide VAPT training?
Yes. VAPT training can cover vulnerability assessment, penetration testing, web application security, network security, API security, security tools, vulnerability validation and professional reporting.
Do you provide ISO/IEC 27001 training?
Yes. Training can cover ISO/IEC 27001 fundamentals, ISMS implementation, risk assessment, risk treatment, controls, Statement of Applicability, internal auditing and certification preparation.
Do you provide PCI DSS training?
Yes. PCI DSS training can cover PCI DSS fundamentals, cardholder-data protection, security controls, vulnerability management, security testing, compliance preparation and gap assessment.
Do you issue ISO/IEC 27001 certification?
Training providers do not automatically issue official ISO/IEC 27001 certification. Formal certification is obtained through the appropriate certification process with a recognized certification body.
Do you issue PCI DSS certification?
PCI DSS validation depends on the applicable assessment requirements and qualified assessment process. Training and consulting should not be confused with formal PCI DSS validation or attestation.
Can companies request private training?
Yes. Organizations can request customized cybersecurity, VAPT, ISO/IEC 27001, PCI DSS or cybersecurity-awareness training for their teams.
Can beginners take VAPT training?
Yes. Training can be structured according to the participant’s existing technical knowledge and experience.
About the Author
Jackson Godwin is a Cybersecurity Consultant and Vulnerability Assessment & Penetration Testing (VAPT) Specialist with over five years of professional experience in cybersecurity.
His areas of expertise include:
- Vulnerability Assessment & Penetration Testing (VAPT)
- Web Application Security
- Network Security
- Cloud Security
- Governance, Risk & Compliance (GRC)
- ISO/IEC 27001
- PCI DSS
- AI Security
- Cybersecurity Awareness
- Security Consulting
Jackson has experience working across cybersecurity assessment, penetration testing, security auditing, compliance and risk-management activities.
He is also the founder and author of JacksonTechnology.com.ng, a cybersecurity-focused platform publishing practical security guides, cybersecurity awareness stories, ethical hacking resources, certification and career guides, open-source cybersecurity tool guides, AI security content and cybersecurity education.
His goal is to make cybersecurity knowledge more accessible to students, IT professionals, businesses and everyday technology users while helping organizations better understand and manage their cybersecurity risks.
Start Your Cybersecurity Journey
Whether you are an individual looking to develop practical cybersecurity skills or an organization looking to improve its security posture, the right training and assessment can provide a strong foundation.
From VAPT and penetration testing to ISO/IEC 27001, PCI DSS, cybersecurity awareness and GRC, our goal is to provide practical, understandable and security-focused education and support.
Ready to discuss your training or cybersecurity requirements?
Contact us today to request training information, a customized corporate training program, or a cybersecurity assessment quotation.