
By Jackson Godwin. Cybersecurity Analyst & Penetration Tester.
Disclaimer
Hey folks – Amass is a powerful tool for authorized bug hunting and security research! Always make sure you have proper permission before using it on any target. Stay ethical, stay legal, and happy hunting!
Hey everyone! Today, we’re diving into Amass – one of the most powerful subdomain discovery tools you’ll find in Kali Linux. Brought to you by OWASP, Amass is a beast when it comes to mapping out subdomains using both passive and active techniques. It pulls data from a wide range of sources, giving you a comprehensive view of your target’s external attack surface. If you’re into bug bounty or authorized security testing, this is a tool you absolutely need to know. Let’s get started
Insallation
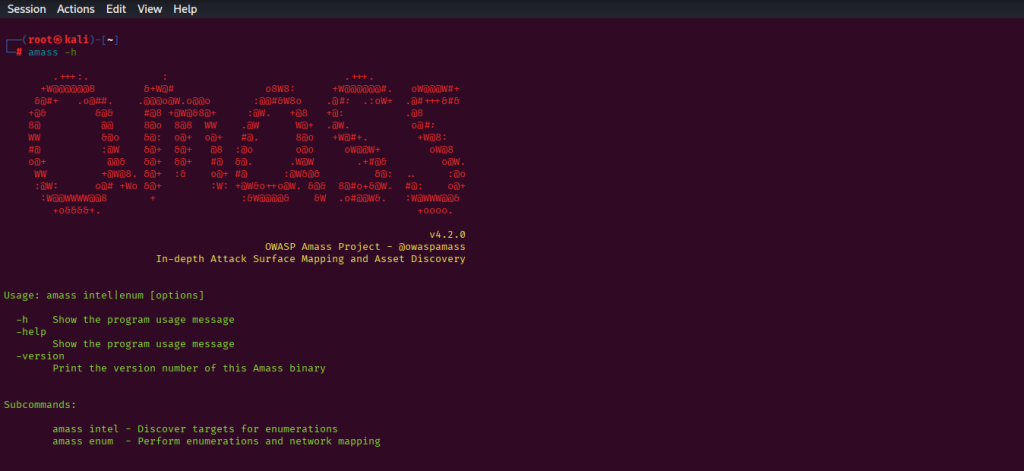
The tool is pre-installed on Kali Linux
amass -h
Using Amass – Practical Examples with VulnWeb
For this tutorial, we’ll use testphp.vulnweb.com – a deliberately vulnerable web application hosted by Acunetix for educational and security testing purposes. This is a safe, authorized environment for practicing subdomain enumeration.
Note:
vulnweb.comis a publicly available testing ground. Always ensure you have proper authorization before scanning any target.
Basic Subdomain Enumeration (Passive Mode)
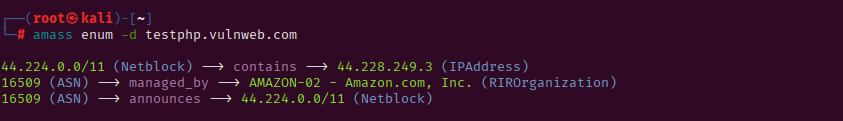
To perform a passive subdomain discovery scan on the target domain:
amass enum -d testphp.vulnweb.com
Passive Enumeration with Verbose Output
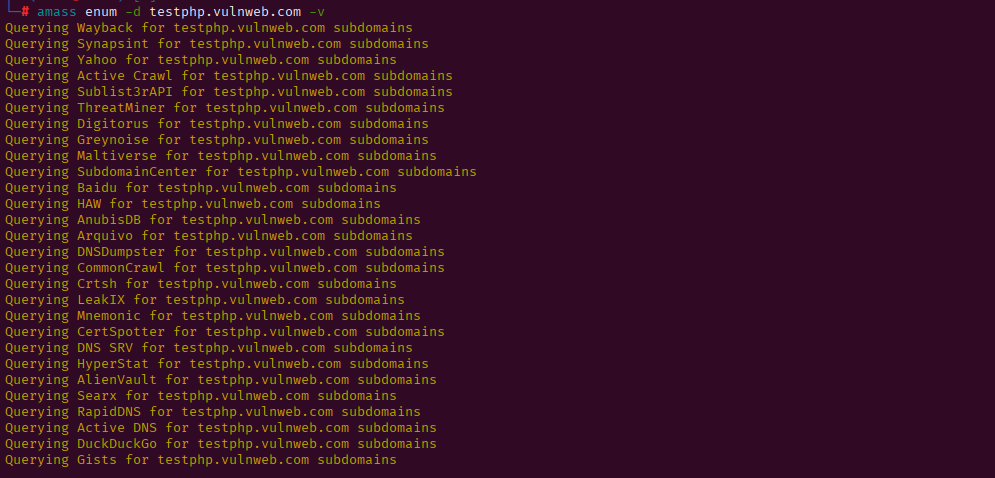
To get more detailed information about the enumeration process and discovered subdomains:
amass enum -d testphp.vulnweb.com -v
Disclaimer
This tutorial and the Amass tool are provided for educational and informational purposes only. Amass is a subdomain discovery tool intended for use in authorized bug bounty programs, security assessments, and legitimate reconnaissance activities. The author does not endorse or encourage any unauthorized or malicious activities. Users are solely responsible for ensuring they have proper authorization before using this tool and for complying with all applicable laws and regulations. vulnweb.com It is used here as an authorized educational testbed.