Working with Steganography Tools – Data Concealment and Password Recovery in JPEG Images
July 23, 2026
Com 0
By Jackson Godwin. Cybersecurity Analyst & Penetration Tester.
Hey everyone! If you’ve ever tackled a CTF challenge, you know that steganography often comes in handy for finding hidden hints or keys. GitHub is full of tools for this, but today we’re highlighting two that are particularly useful for your CTF lab setups
Tools for Steganography
Steghide – To hide a string or key in any file format.
Stegbrute– To crack a password and extract a string from a JPEG file.
Let’s take a look 😛 !!
Stegbrute Tool Installation
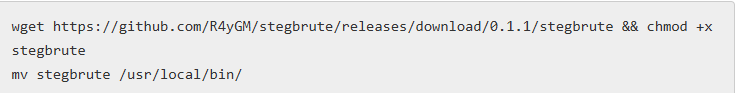
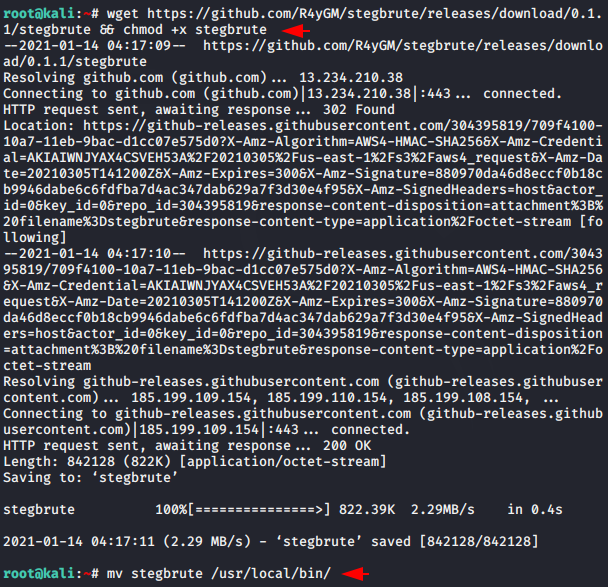
Stegbrute is a fast steganography brute force tool written in Rust using also threads to achieve a faster execution. This is not a pre-installed tool, so we have to install it first using the wget command and then move it to the binary folder to access it from anywhere.
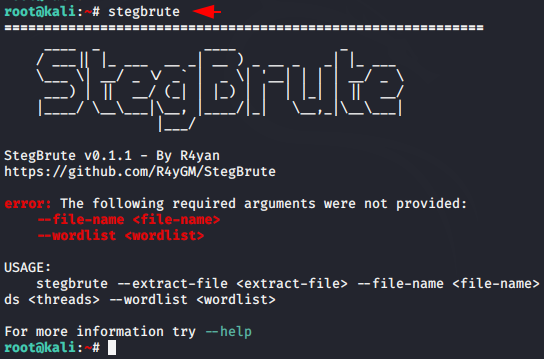
Done 😛 !! As you can see in the image below, we can now use this tool just by entering the name.
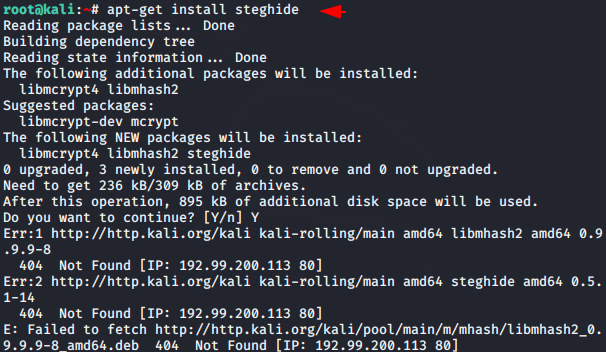
Steghide is a steganography program that is able to hide data in various kinds of image and audio files. The tool is already connected to the Kali Linux repository, and that is why we can install it using the “apt-get” command.
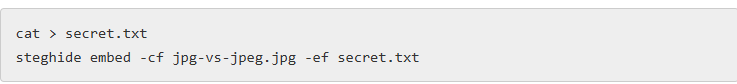
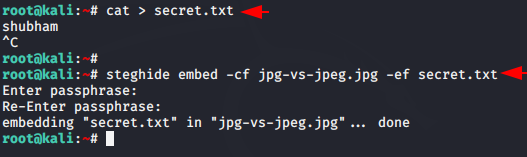
Done 😛 !! Both tools are now successfully installed to demonstrate an example of steganography. First, we will create a text file, hide the text file in a JPEG file using the Steghide tool, and protect it with a password.
Usage 😛 !! steghide embed -cf < JPEF file > -ef < File that you want hide >
Amazing 😛 !! As we know, the Stegbrute tool uses a wordlist to extract hidden content from the file. Now all you have to do is to give this tool the location of the JPEG file and the wordlist, and immediately after that, it will try to crack it using multiple passwords. After the password is successfully cracked, we get the secret string in the result file that we previously hid.
In the same way, you can hide any secret key and use these tools to prompt the user in your CTF labs
About the Author
Jackson Godwin is a Cybersecurity Consultant specializing in Vulnerability Assessment and Penetration Testing (VAPT), Governance, Risk and Compliance (GRC), ISO 27001, PCI DSS, Cloud Security, and Enterprise Security. Through JacksonTechnology.com.ng, he shares practical compliance guides, cybersecurity tutorials, penetration testing resources, and security best practices to help organizations strengthen their cyber resilience.